Telecoms minister Ian Murray told the Sky News Defence Insider app that he would move "as quickly as possible" to update the law and ensure far greater punishments can be imposed on hostile actors who target such infrastructure, which carries the bulk of the nation's data and gas supplies.
Proposed sanctions include extending a maximum prison term from 5 to 14 years, and the ability to impose unlimited fines.
Russia has been accused of conducting a covert operation over cables and pipelines in waters north of the UK, using three submarines.
Any updated legislation would not be used against hostile states.
However, the Kremlin is believed to hire criminals and other proxies to conduct acts of sabotage on its behalf. The law would apply to such individuals.
Mr Murray said he hoped that the prospect of such a length prison term would act as a deterrence. You can see his full interview here.
"Undersea cables are the hidden backbone of modern Britain, carrying the data we rely on every day to message friends and family, do our banking, and run our businesses," the minister said separately in a statement.
"The threats we face have changed dramatically, with suspicious Russian activity around critical undersea infrastructure, yet some of the laws protecting these vital connections date back more than a century.
"We intend to modernise those laws with tougher penalties, stronger requirements on industry and new powers to protect our national security, making sure the UK's critical infrastructure is fit for the threats of today and tomorrow."
More from Sky News:
Will approved North sea drilling plans bring down energy bills?
Vital clues could help predict prostate cancer years in advance
Fibre-optic cables running along the seabed carry around 99% of the UK's international data, underpinning everything from messages and video calls to online banking and shopping.
Any significant disruption in this flow of data would risk derailing daily life and could have a devastating impact on the economy.
The same is true for any attack against the UK's undersea pipelines that provide 74% of the nation's gas supply as well as its grid of undersea electricity cables.
In its push to update legislation governing underwater infrastructure, which dates back to 1885, the government is publishing a white paper on Thursday that sets out its proposals, which also includes requiring the companies that provide the subsea cables and pipelines to do more to identify sabotage and espionage risks.
The government is seeking views on the document from industry and other experts over the next 12 weeks.
Mr Murray said the legislation would be updated in the current parliament.
It follows cases in which several notorious murderers avoided facing up to the judge.
The law has already been changed to allow an extra two years for those who refuse, but the Ministry of Justice (MoJ) admitted it's "little deterrent" to people on a very long sentence.
Ministers hope the new penalties will be a tougher deterrent and give offenders "something more to lose".
The MoJ said the plans will allow crown court judges to impose the following penalties:
- Loss of prison privileges for almost three months (84 days)
- Cellular confinement for up to three weeks (21 days)
- Loss of social visits for nearly a month (27 days)
- Restrictions on social visits to once every four weeks, for almost three months (84 days)
Killers who disrupt their sentencing hearing will be subject to the same consequences.
Visits from prisoners' children will be exempt in cases where it's in the child's best interests.
Eighteen to 20-year-olds in young offender institutions will also only face up to 10 days' confinement, while the removal of other privileges will be capped at 21 days.
The MoJ said no penalty can guarantee prisoners attend sentencing but the new rules will "strengthen the consequences".
"Criminals should not be able to pick and choose when they face justice," said prisons minister Catherine McKinnell.
"Refusing to turn up to sentencing is an insult to victims and their families, and offenders must face the consequences."
The victims' commissioner for England and Wales, Claire Waxman, also welcomed the move.
She said the announcement was testament to "the tireless efforts of victims' families who refused to accept that offenders could simply opt out of facing justice".
More from Sky News:
Ex DUP leader accused of raping woman inside parliament
Websites across Europe taken down to protect systems
Ms Waxman added: "Having worked with the families of Sabina Nessa, Zara Aleena and Jan Mustafa, I know how offenders' refusal to attend sentencing hearings compounds trauma and robs families of one of the very few moments of accountability in the justice process.
"Their determined campaigning, alongside that of Olivia Pratt-Korbel's family, helped ensure that this harm could no longer be ignored."
Other killers who have refused to attend sentencing include triple crossbow killer Kyle Clifford, while Southport knifeman Axel Rudakubana was removed from court after shouting and claiming he felt ill.
The plans will be introduced to parliament on Thursday and should come into effect next year.
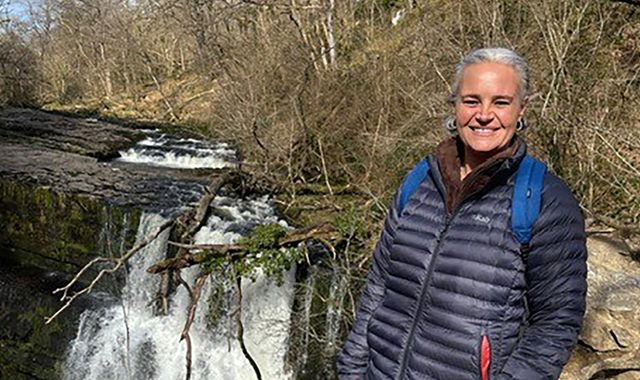
Eleanor Barnfield, 47, died in hospital after her car collided with a wall on Coity Road in Bridgend on Monday afternoon.
In a statement, South Wales Police said she had sustained "puncture wounds unrelated to the collision".
A 61-year-old man from Bridgend has been arrested on suspicion of murder following an investigation around Ger-y-Nant, a housing complex managed by the Valleys to Coast housing association where Ms Barnfield worked.
Ms Barnfield's family paid tribute to "the kindest, most loving, bravest person in the world".
They added: "She meant everything to us and will be forever loved and missed deeply by her devoted family and friends. She was our rock."
South Wales Police Chief Superintendent Jason Rees urged people not to speculate online about the circumstances of Ms Barnfield's death.
He said: "Our thoughts remain firmly with Eleanor's family.
"I want to assure the community that teams of detectives and specialist staff are investigating.
"We appreciate the patience and support of residents, especially those displaced following the incident.
"Local communities may notice an increased police presence as our investigation continues."
Meanwhile, Welsh Ambulance Service said it was aware of "contradictory and misleading rumours regarding a delayed ambulance response", but insisted these were "factually untrue".
More from Sky News:
'Wave of attacks' feared after websites hit by 'critical' flaw
Vaping study raises health concerns
An 'unimaginably difficult time'
Valleys to Coast housing association chief executive Jo Oak said the organisation was "devastated by the tragic death of our colleague".
Ms Oak added: "Eleanor was a much-valued member of the Valleys to Coast team, and her loss has been deeply felt by everyone who knew and worked alongside her.
"She made an important contribution to our organisation and to the communities we serve, and she will be remembered with great warmth and affection by her colleagues.
"Our thoughts and deepest sympathies are with Eleanor's family and friends at this unimaginably difficult time.
"We are doing everything we can to support those affected by her loss."
Police have asked anyone with relevant information to contact them.
According to a poll, 79% of people think it's "unfair" they have to pay, while those in other UK nations do not.
One in 10 people also say they have gone without medicine due to the £9.90 prescription cost.
The survey of 1,781 adults was carried out for the National Pharmacy Association (NPA), which represents about 6,000 independent pharmacies across the UK.
It called prescription fees a "cruel tax on illness" and wants the chancellor to scrap them in next week's budget to help ease cost-of-living pressures.
Prescription charges ended in Scotland in 2011, in Northern Ireland in 2010, and in Wales in 2007.
Some prescriptions in England remain free, including contraception and medicine for hospital inpatients.
Under-16s and over-60s also do not pay, plus 16-18-year-olds in full-time education, some people on benefits, and people with medical conditions including cancer, diabetes and epilepsy.
"It is a national scandal and deeply unfair that anyone could consider stopping vital medicines because of cost," said NPA chairman Olivier Picard.
"This cruel tax on illness, where some patients are exempt but others are forced to pay simply because they have the wrong kind of illness, undermines the founding principles of the NHS."
A number of charities are also backing the campaign.
Marianne Radcliffe, chief executive of Chron's and Colitis UK, said people with ongoing health problems "should not be forced to choose between their health and their finances simply because they need medication every day".
Asthma and Lung UK said patients with respiratory conditions were "essentially paying for their right to breathe", as they are not on the NHS exempt list.
"Being able to take medication shouldn't come down to whether or not you can afford it," said chief executive Sarah Sleet.
More from Sky News:
'Millions' of exploitation attempts as 'critical' flaw hits websites
Poland: Preparing for the worst as Moscow tensions rise
Some 11.6 million people paid for prescriptions last year, according to the NPA.
However, about 3.3 million used a prescription prepayment certificate (PPC), which can work out cheaper than paying for individual items.
It covers all of a person's prescriptions and costs £32.05 for three months or £114.50 for a year.
People may also be able to get free prescriptions through the NHS low income scheme.
The Department of Health and Social Care spokesperson said: "Almost nine in 10 NHS prescriptions in England are currently supplied free of charge.
"For those people who do pay for their prescriptions, we have frozen prescription charges for the last two years, keeping costs as low as possible for millions of patients.
"Every penny raised from prescription charges goes back into our NHS, to support the front-line care from which we all benefit."
A number of government and business websites went offline on Wednesday as a security measure after an urgent software update was issued over vulnerabilities in PHP, a programming language used extensively across the internet.
The developers of PHP said that a set of new updates fixing two previously identified critical vulnerabilities was now live, and strongly encouraged users to update software immediately.
Cloudflare CEO Matthew Prince wrote on X: "In the 10 hours before it was publicly announced, across the network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within two hours, and millions now."
Amazon Web Services also said this flaw is now "being broadly exploited in the wild" - and has revealed that suspected hackers tried to capitalise on the vulnerability days before it was publicly announced.
This comes after an expert told Sky News that disruption will likely become "more widespread" as opportunistic hackers attempt to strike companies trying to patch the fault.
Cyber security officials have said that those unable to apply the fixes should consider temporarily taking their websites down.
Alp Toker, a cyber security expert and director at NetBlocks, called the issue "highly impactful" - and warned the disruption caused by nefarious actors, which has so far been "limited", could become "more widespread".
Speaking to Matt Barbet on The World, Mr Toker explained that the incident "means that anybody on the web can essentially access your web server if you're running the [PHP] software".
He said that the risk had been "very limited because the people who found the vulnerability kept it under wraps for quite a while, but in the last few days it has been seen in the wild".
Mr Toker added that AI agents could "reproduce the attack much more easily", warning that it is "just the beginning of a wider wave of attacks".
"These systems are going to continue to get compromised - month after month, year after year," he said.
'Critical security issues'
Websites linked to governments across Europe went offline on Wednesday as organisations rushed to protect their systems, although some are now back up and running.
In the UK, the Office for Budget Responsibility (OBR) said it had taken its website offline "in view of the critical security issues affecting PHP".
Oxfordshire County Council and Hillingdon Council both separately said they had temporarily taken down their websites as a precaution while they investigate.
A UK government spokesperson said work was under way to "identify and patch any potential exposure".
They added: "We encourage all organisations - private and public, large and small - to follow guidance issued by the NCSC to understand their exposure and take the necessary actions to safeguard their systems."
Meanwhile, the US National Security Agency and the Australian Cyber Security Centre both urged organisations to remain vigilant and apply updates where possible.
The Wikimedia Foundation, which runs online encyclopaedia Wikipedia, was one company on Wednesday that said it was in the process of addressing security vulnerabilities in the PHP programming language.
More from Sky News:
Why is Poland reopening Cold War bunkers?
Law must be updated to protect 'backbone' of UK
PHP widely used
PHP is used by almost 70% of websites, according to cyber security firm Cloudflare, and underpins popular platforms such as WordPress and Magento.
It said the two vulnerabilities found, which AI agents helped to uncover, were rated 9.2 out of 10 on the CVSS v4.0 severity scale.
OpenAI, which runs ChatGPT, said it has been leading a team of researchers to address the flaw in PHP over the past two months - and supported its developers as it led the fixes.
The company called the incident "one of the most impactful security issues in recent memory", adding that while AI can help to uncover issues, it can also aid attackers.
On Tuesday, the European Union Computer Emergency Response Team (CERT-EU) said the 9.2 rating indicated a risk of unauthenticated remote code execution, a type of flaw that could allow attackers to run malicious code on vulnerable systems without logging in.
It urged organisations to prepare for the immediate patching of affected assets.